Managed IT Support
Full-spectrum workstation stewardship, reliable help desk assistance, automated operating system patching, and structured IT asset management tailored to your operational pace.
IT That Keeps Your Business Moving. We deliver proactive technology support, monitored infrastructure, cloud systems, resilient backup strategies, and layered cybersecurity defense engineered specifically for small and midsized businesses.
Transparent Engineering Notice: We do not offer exaggerated claims such as “100% impenetrable security” or “zero-risk operations.” Modern technology resilience is achieved through defense-in-depth, disciplined patch cycles, verified backup integrity, continuous endpoint monitoring, and rapid incident response protocols.
Every business environment requires continuous visibility, robust access governance, resilient data pipelines, and responsive technical stewardship.
Full-spectrum workstation stewardship, reliable help desk assistance, automated operating system patching, and structured IT asset management tailored to your operational pace.
Continuous threat detection telemetry, behavioral endpoint protection, MFA policy enforcement, vulnerability prioritization, and structured incident response planning.
Systematic migration planning, secure hybrid configuration, cloud identity federation, SaaS tenant hardening, and cloud cost control for modern SMB environments.
Firmware governance, secure VLAN segmentation between guest and operational hardware, Wi-Fi performance tuning, firewall filtering, and encrypted site-to-site tunnels.
Resilient 3-2-1 backup architecture, immutable cloud snapshots, realistic RPO/RTO engineering, periodic restoration testing, and documented continuity runbooks.
Behavioral endpoint telemetry, whole-disk encryption enforcement, USB restriction policies, rapid quarantine mechanisms, and continuous configuration hygiene.
Explore our illustrative operations telemetry framework showing how business systems, patch status, network pathways, and backup verifications are monitored and evaluated.
Evaluate your organization’s current posture, estimate resource allocations, and benchmark security maturity using our interactive planning utilities.
Review nine crucial controls across MFA, patch governance, backups, and employee protocol. Your progress automatically persists locally in your browser.
Open Checklist Tool →Score your operational risk across categories including device sprawl, cloud usage, support responsiveness, and data compliance considerations.
Run Readiness Assessment →Model required storage volume, determine target Recovery Point and Recovery Time Objectives, and outline cloud snapshot frequencies.
Configure Backup Plan →Explore an illustrative operating expenditure estimate based on user count, device volume, cloud footprint, and required support coverage.
Estimate Technology Costs →
Small and midsized businesses are the economic foundation of modern industry, yet they face the exact same digital vulnerabilities as large global enterprises. Our approach bridges this gap without overwhelming complexity.
Every device, user token, and external API connection is continuously verified. We implement least-privilege policies to ensure that compromised credentials cannot easily pivot across your network.
Silent hardware failures and unpatched vulnerabilities cause the vast majority of operational downtime. Our monitoring provides transparent telemetry across endpoints and network gateways.
Security measures reduce risk, but resilient backups guarantee operational survival. We design isolated, immutable storage solutions engineered to recover mission-critical data quickly.
Eliminate operational friction, stabilize staff workstations, and protect organizational productivity with structured IT management, fast response help desk support, and proactive maintenance.
When your team experiences technical disruptions, your business loses momentum. Our Managed IT services provide dependable technical leadership, structured maintenance schedules, and empathetic user support so your employees can concentrate on core business goals.
We act as your dedicated IT department or supplement your internal technical staff with specialized infrastructure management, automated patching, software license oversight, and technology procurement.
Direct ticket submission, remote screen assistance, and clear communication on issue resolution progress without technical jargon.
Streamlined onboarding procedures ensuring new hires receive correct permission levels, and departing employees lose access instantly.
Automated deployment of security fixes for Windows, macOS, and critical third-party software, staged to minimize disruption.
Strengthen your defenses against phishing, ransomware, credential abuse, and operational disruption. We implement multi-layered safeguards designed specifically for small and midsized business risks.
Cybersecurity should protect business operations, not paralyze them. Rather than relying on single antivirus products, we construct defense-in-depth across your identity providers, employee endpoints, network boundaries, and cloud applications.
We focus on reducing attack surfaces, enforcing multi-factor authentication (MFA), monitoring endpoint activity for anomalies, and equipping your personnel with realistic threat recognition skills.
MFA everywhere, strong password rules, single sign-on (SSO), and role-based privilege restriction.
Full-disk BitLocker/FileVault encryption, behavioral telemetry, rapid host isolation, and USB storage management.
Segmented guest and IoT networks, stateful firewall inspection, DNS filtering, and encrypted administrative access.
Anti-spoofing protocols (SPF, DKIM, DMARC), email quarantine filters, external forwarding bans, and link defense.
Immutable snapshot vaults, automated off-site synchronization, periodic integrity audits, and offline recovery drills.
Design, deploy, and govern secure cloud infrastructure tailored to your business operations. Maximize uptime, simplify remote collaboration, and prevent cloud configuration drift.
Moving to the cloud offers tremendous agility, but default cloud configurations frequently leave critical security gaps open. We guide businesses through sensible migrations, harden SaaS tenants, and maintain structured access controls across all your platforms.
Whether you are modernizing your Microsoft 365 environment, hosting line-of-business applications in private cloud virtual machines, or architecting a hybrid setup with on-premises equipment, we build stable and predictable cloud solutions.
High-performance Wi-Fi, structured switching, firewall governance, and network segmentation engineered to prevent bottlenecks and isolate vulnerabilities.
Your local and wireless network is the critical conduit through which every customer call, file transfer, and database transaction moves. When network switches fail or Wi-Fi coverage drops, overall productivity plummets.
We design, configure, and monitor enterprise switching, business Wi-Fi access points, and next-generation firewalls to ensure dependable throughput, prioritized voice traffic, and robust logical isolation between guest devices, office workstations, and sensitive servers.
When hardware burns, ransomware encrypts files, or human error occurs, your backup architecture determines whether your business continues or halts. We engineer tested recovery pipelines with defined RTO and RPO metrics.
Many organizations assume their backups work because a daily scheduled job reports “successful”—only to discover corrupted snapshots or untested restoration pathways during a genuine crisis.
We replace false assumptions with disciplined engineering. We help you establish realistic Recovery Point Objectives (how much recent data you can afford to recreate) and Recovery Time Objectives (how many hours before systems must be back online), and we routinely test file and bare-metal restores to confirm viability.
The maximum acceptable age of files that must be recovered from backup storage for normal operations to resume.
The maximum acceptable duration of time that a system can be offline before serious business damage occurs.
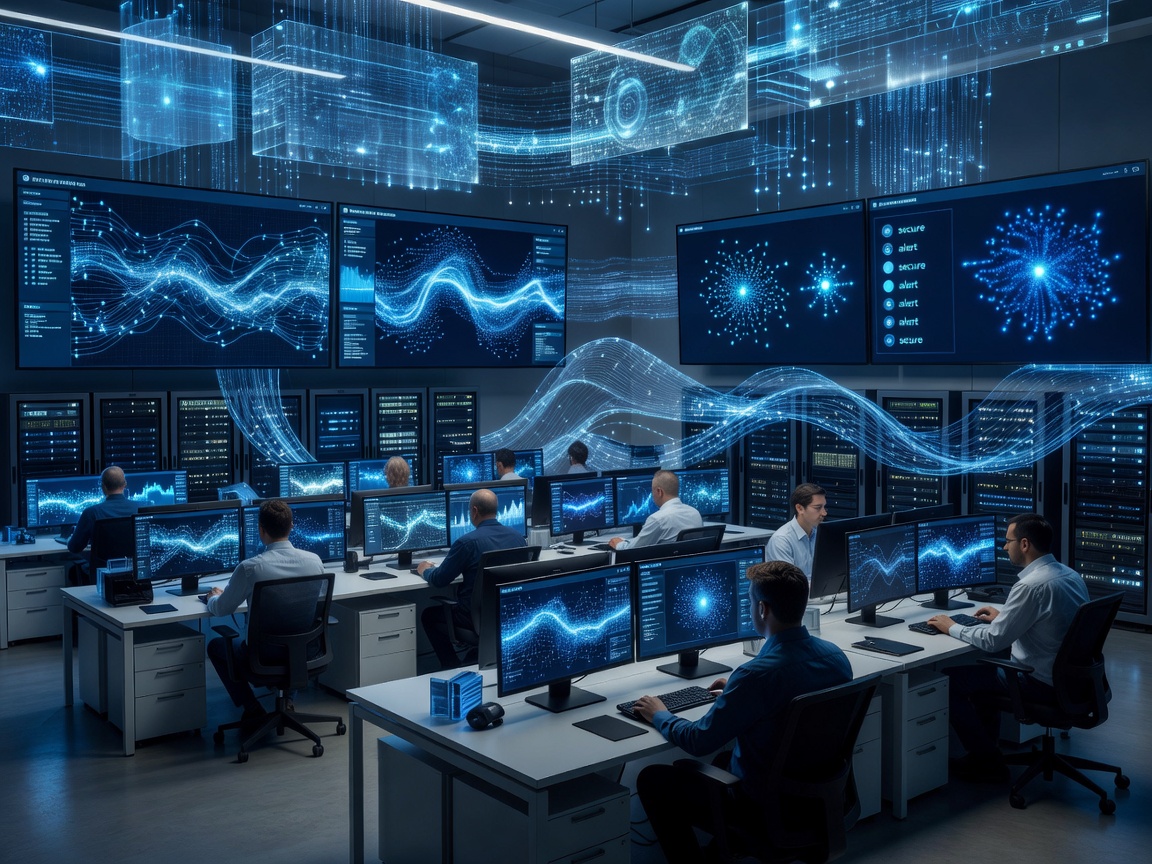
Experience our operations monitoring framework. Below is a simulated operations command console illustrating how endpoint health, security telemetry, network throughput, and backup verifications are continuously monitored and evaluated.
Continuous authentication monitoring with conditional access enforcement, MFA token verification, and automated legacy protocol blocking.
In traditional break-fix IT, technicians only respond after a server has crashed, an employee is locked out, or ransomware has encrypted files. Our operations console operates on continuous telemetry that detects pre-failure symptoms:
Every employee laptop, remote workstation, and administrative tablet is a potential entry point for attackers. We enforce strong host controls, encryption, and automated updates.
With hybrid work now the standard for small and midsized businesses, physical perimeters have largely dissolved. Corporate laptops operate from home Wi-Fi networks, hotel conference rooms, and client offices.
We provide centralized endpoint protection that safeguards machines wherever they connect, isolating compromised hosts with one click, enforcing storage encryption, and ensuring patches are applied even when employees are traveling.
Evaluate your organization’s current cybersecurity and infrastructure posture across eight critical operational domains. Receive an educational risk summary, maturity tier, and prioritized remediation actions.
Our scoring model evaluates the balance between proactive defense and recovery readiness. In modern cybersecurity, prevention alone is insufficient—an organization with perfect antivirus but untested backups remains highly vulnerable to ransomware extortion.
By evaluating identity, endpoints, network segmentation, email hygiene, and backup immutability together, we identify the exact vulnerabilities attackers exploit first.
Ensure your business can survive power outages, hardware failures, cyber incidents, and vendor outages with structured operational contingency runbooks.
Having a backup of your data is critical, but if you do not have replacement hardware, cloud failover servers, or secondary communications channels, your business remains frozen.
Business continuity planning addresses the entire operational ecosystem: where your staff works if the office is inaccessible, how payments are processed during Internet service provider outages, and how emergency decisions are communicated.
Executive-level technology roadmapping, budget optimization, regulatory IT alignment, and vendor contract reviews designed for organizations without a full-time Chief Information Officer.
Technology should be a clear driver of competitive efficiency rather than an unpredictable cost center. Our consulting engagements provide practical leadership to guide your digital investments.
We evaluate upcoming commercial milestones, review legacy software platforms, and deliver pragmatic roadmaps that balance modern security controls with budget realities.
Every vertical operates with unique compliance constraints, workflows, and operational risks. We architect solutions addressing the exact requirements of your industry.
Confidential client file security, billable hour continuity, document management encryption, and strict remote work access governance.
Priority: Data ConfidentialityStrict access segregation, financial data encryption in transit and at rest, multi-factor authentication, and compliance audit log archiving.
Priority: Regulatory RecordkeepingPatient record integrity, medical imaging server resilience, workstation auto-lock protocols, and HIPAA security rule alignment assistance.
Priority: Protected Health InformationProduction line network isolation, shop-floor workstation stability, IoT device separation, and supply chain ERP uptime maintenance.
Priority: Operational UptimePoint-of-sale network segregation, PCI DSS foundational alignment, redundant store internet connections, and inventory database syncing.
Priority: POS Transaction UptimeSecure guest Wi-Fi separation from booking systems, property management system stability, and administrative credential controls.
Priority: Guest Network IsolationWire-fraud defense controls for escrow communications, mobile agent laptop protection, and cloud document signature management.
Priority: Wire Fraud MitigationWarehouse dispatch system availability, mobile barcode scanner Wi-Fi coverage, and fleet GPS telemetry gateway stability.
Priority: Dispatch ContinuityDeveloper workstation posture, code repository multi-factor enforcement, cloud environment isolation, and identity federation.
Priority: Source Code ProtectionJob-site cellular connectivity, rugged field tablet management, cloud blueprint syncing, and subcontractor email phishing defenses.
Priority: Field Mobility & SyncExplore realistic conceptual scenarios demonstrating how we solve complex technology challenges for small and midsized business environments.
Authoritative, practical technical resources designed to help business owners, operations directors, and office managers make informed technology decisions.
Moving beyond the obsolete “break-fix” model. Why proactive patch management, automated monitoring, and regular lifecycle reviews reduce operational disruption.
Why SMS codes are vulnerable to SIM swapping and interception, and how app-based push notifications and hardware security keys deliver true authentication resilience.
Understanding the mathematical and operational differences between Recovery Point Objective and Recovery Time Objective, and how to balance recovery speed against costs.
The shared responsibility model explained: why cloud providers guarantee platform uptime, but leave customer data protection and accidental deletion recovery in your hands.
A technical blueprint for minimizing lateral movement, establishing immutable offline storage, and creating incident isolation playbooks that avoid ransom extortion.
How splitting your network into isolated virtual compartments keeps smart TVs, guest smartphones, and heating controllers away from sensitive accounting records.
Explore self-service calculators, security audits, and architectural evaluators designed to provide actionable clarity on your infrastructure, compliance, recovery, and budget.
Audit nine crucial security controls across MFA, patch cycles, immutable backups, and staff offboarding. Automatically saves your progress in your browser.
Calculate your organization’s security health score across eight crucial operational domains and receive tailored remediation steps.
Analyze your workforce model, server arrangements, and support structure to receive a tailored operational blueprint and risk analysis.
Model business data volumes, specify criticality tiers, configure retention rules, and calculate required local and immutable cloud storage.
Determine whether your applications, databases, identity systems, and connectivity are optimized for pure cloud or hybrid cloud operations.
Estimate realistic monthly technology operating costs based on user counts, server footprints, physical locations, and security coverage tiers.
Review nine essential baseline security controls. Check the items your organization has implemented. Your progress automatically persists in your browser’s local storage.
Evaluate your technical infrastructure across device counts, cloud footprint, support models, and network complexity.
Model your company’s estimated data volume, select target recovery objectives, and generate an illustrative backup architecture.
Determine whether your applications, line-of-business databases, and internet bandwidth are primed for full cloud migration or hybrid architecture.
Model illustrative technology budgeting requirements based on staff counts, device complexity, and required security safeguards.
Engineered to deliver enterprise-grade infrastructure resilience, disciplined cybersecurity monitoring, and responsive technical support for small and midsized businesses.
Founded on the belief that growing businesses deserve the same architectural rigor and security monitoring as global corporations, temponestbackstag.com operates as a dedicated technology partner.
We reject the outdated break-fix mentality where IT firms only profit when systems collapse. Instead, we align our success with yours through continuous monitoring, proactive maintenance, automated vulnerability patching, and resilient backup systems.
Our team values clarity and technical honesty. We avoid fear-based cybersecurity sales tactics, and we never make absolute promises like “100% unbreakable defense.” Instead, we build multi-layered security architectures that tangibly reduce operational risk and allow your business to bounce back rapidly when disruptions occur.
Legal Name: TempoNest Technology Operations Ltd.
Company Registration No: 14892019
Registered Office: 71-75 Shelton Street, Covent Garden, London, WC2H 9JQ, United Kingdom
Official Contact Email: [email protected]
Brand Domain: temponestbackstag.com
Engage directly with an enterprise-experienced infrastructure and cybersecurity architect. We evaluate your operational bottlenecks, audit defense gaps, and design a pragmatic technology roadmap tailored to your business scale.
Review of user headcounts, server deployments, cloud tenants, network perimeter, and legacy software dependencies.
Evaluating MFA policy coverage, patch intervals, backup immutability, and endpoint encryption compliance.
Establishing achievable RPO and RTO thresholds, offsite replication pipelines, and emergency failover protocols.
Delivering an executive-level technology roadmap with transparent predictable budgeting and phased rollout steps.
Submit your details to be matched with the relevant technology specialist. All inquiries are treated under mutual NDA standards.
Last Updated: January 1, 2026. Comprehensive documentation on data protection, retention, and processing standards.
TempoNest Technology Operations Ltd. (“temponestbackstag.com”, “we”, “our”, or “us”) is dedicated to maintaining the confidentiality, integrity, and availability of personal information entrusted to us. This Privacy Policy details how we collect, process, store, and safeguard personal and business data through our website (temponestbackstag.com), interactive planning tools, simulated operations consoles, and general commercial communications.
We operate in strict accordance with applicable data privacy legislation, including the UK General Data Protection Regulation (UK GDPR), the Data Protection Act 2018, the EU GDPR, and relevant US state privacy statutes including the California Consumer Privacy Act (CCPA) as amended by the CPRA.
We gather information exclusively for legitimate operational, security, and consulting purposes. Data collection categories include:
Under UK and European data protection law, we rely on clear lawful bases for processing personal information:
We do not sell, rent, lease, or monetize your personal information or business infrastructure metadata under any circumstances. In delivering web services and customer consultations, we may engage vetted third-party service providers (“sub-processors”) bound by stringent data protection agreements, including:
When technical information is processed or stored outside the United Kingdom or the European Economic Area (EEA), we enforce recognized cross-border transfer safeguards. These include the UK International Data Transfer Addendum, standard contractual clauses (SCCs) approved by the European Commission, and verifications that destination entities maintain equivalent levels of personal data protection.
As an IT infrastructure and cybersecurity advisory provider, we apply strict internal controls to prevent unauthorized access, alteration, disclosure, or destruction of client records. These measures include:
We retain personal data only for as long as strictly necessary to fulfill the objectives for which it was gathered. Technical inquiries resulting in active commercial engagements are retained for the duration of the agreement plus statutory limitation periods (typically seven years for accounting compliance). General inquiries that do not transition to formal contracts are expunged from our communications databases within twenty-four (24) months.
Depending on your jurisdiction, data protection legislation affords you specific statutory rights regarding your personal information, including:
To exercise any of these statutory rights, please submit a written request to our Data Protection Officer at: [email protected]. We will respond within thirty (30) days without administrative charge.
If you have questions or complaints regarding our privacy practices, you may reach our compliance officers at:
TempoNest Technology Operations Ltd.
Attn: Data Privacy Team
71-75 Shelton Street, Covent Garden
London, WC2H 9JQ, United Kingdom
Email: [email protected]
You also maintain the right to lodge a formal complaint with your relevant supervisory authority. In the UK, this is the Information Commissioner’s Office (ICO) at ico.org.uk.
Last Updated: January 1, 2026. Terms governing the use of temponestbackstag.com, informational resources, and interactive tools.
These Terms of Service (“Terms”) establish an enforceable legal agreement between you (“User”, “Client”, or “You”) and TempoNest Technology Operations Ltd. (“temponestbackstag.com”, “Company”, “we”, or “us”). By accessing our website, interacting with our 3D infrastructure visualizations, utilizing our security self-assessment tools, or submitting consultation inquiries, you express full assent to these Terms. If you do not agree, you must immediately cease accessing this site.
All content, telemetry illustrations, knowledge-base guides, simulated dashboards, and interactive calculators published on temponestbackstag.com are supplied for general educational and informational purposes. While we strive for rigorous technical accuracy:
The layout, visual aesthetics, dark glassmorphism styling, proprietary WebGL shaders, Three.js 3D command center models, code snippets, branding logos, articles, and written copy on temponestbackstag.com are the exclusive intellectual property of TempoNest Technology Operations Ltd. and are protected by United Kingdom and international copyright, trademark, and trade secret laws.
Users are granted a limited, revocable, non-exclusive license to view and print pages from the website for internal commercial planning purposes. You may not scrape, systematically copy, reverse-engineer, distribute, or publicly reproduce our proprietary code, 3D assets, or educational texts without prior written consent.
In accessing temponestbackstag.com, you agree not to:
Any provision of professional Managed IT services, 24/7 security monitoring, cloud migration execution, or backup administration is governed by a distinct, signed Master Services Agreement (MSA) and Service Level Agreement (SLA). The materials presented on this website do not supersede, amend, or modify the terms of any separately executed commercial contract between TempoNest Technology Operations Ltd. and its corporate clients.
Our website and resource articles may contain links to external third-party software vendors, standards bodies, or official regulatory resources (such as CISA, NIST, or the ICO). These links are supplied solely for user convenience. We exercise no administrative control over third-party domains and assume no responsibility for their content, availability, or data processing policies.
To the maximum extent permitted by applicable law in England and Wales:
These Terms and any non-contractual disputes arising from them shall be governed by and interpreted in accordance with the substantive laws of England and Wales. The courts of London, England, shall have exclusive jurisdiction to resolve any legal claims or controversies arising out of or in connection with these Terms or the website.
We reserve the right to revise, update, or replace any part of these Terms at our discretion. Updated versions will be published directly to this URL with a revised “Last Updated” date. Continued interaction with the website following revisions constitutes acceptance of the modified Terms.